

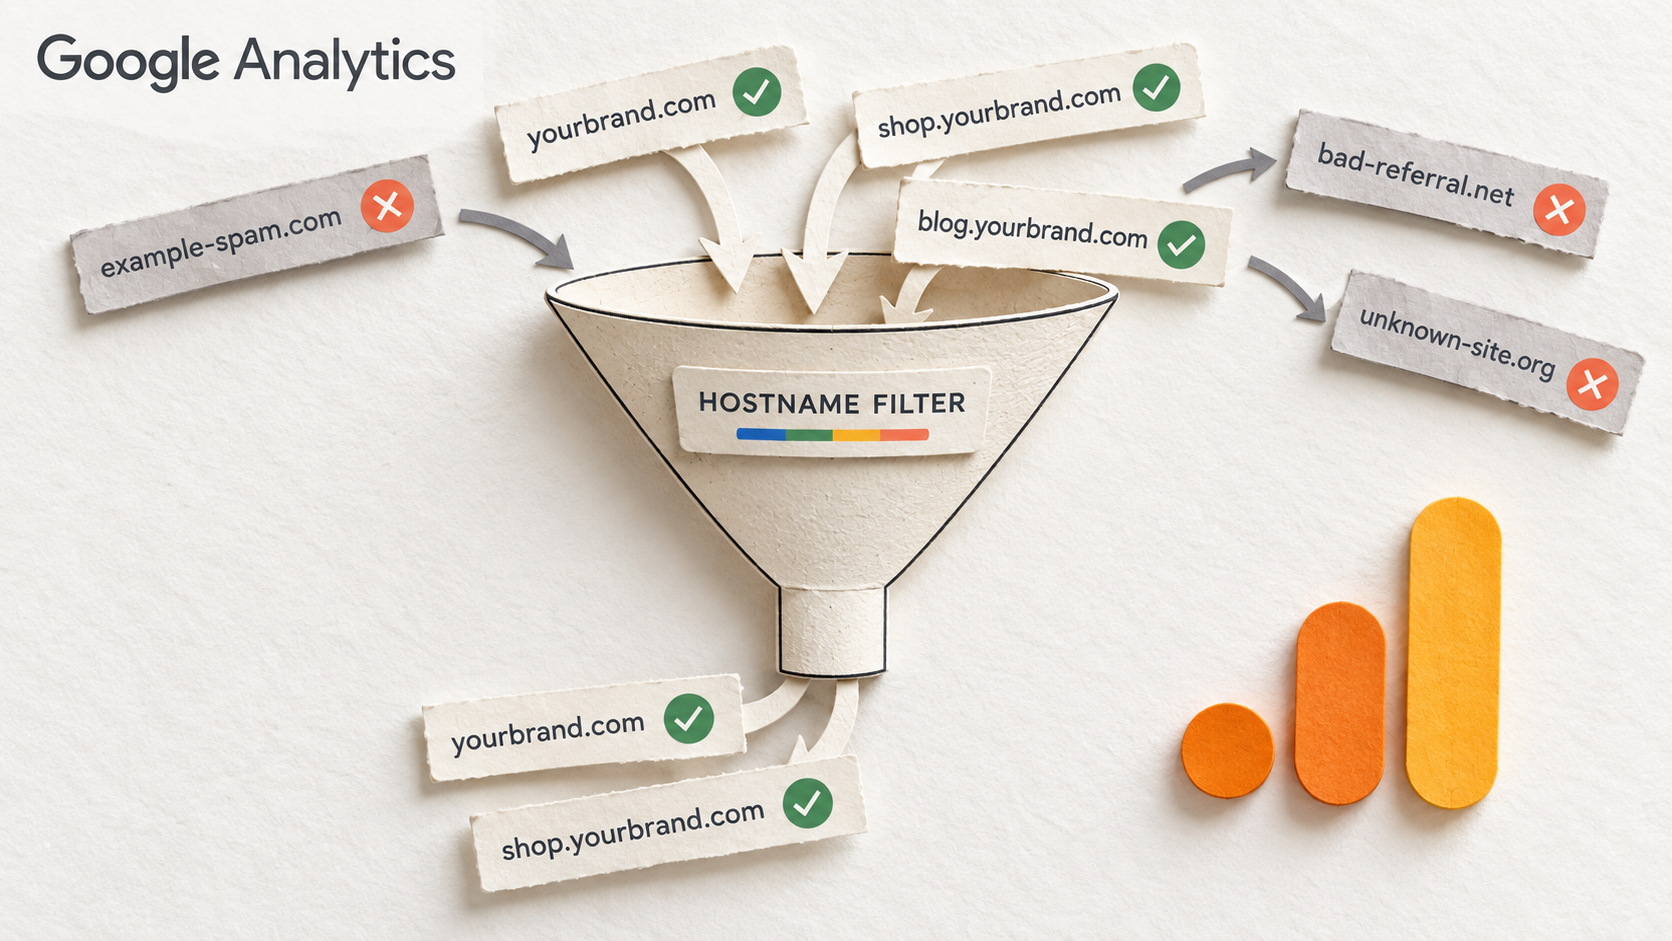
Google Analytics now lets website owners approve the hostnames feeding their reports and filter out events from elsewhere. Announced on September 21, the new Include option reduces the need to keep identifying and excluding unwanted hostnames individually.
The change is relevant to the suspicious Singapore traffic SEW reported on September 18. In one GA4 Realtime snapshot, 365 of 419 active users were listed as being in Singapore. That snapshot showed the scale of the anomaly, but did not establish which hostnames or collection methods were involved. Whether the new filter would catch that traffic remains untested.
What Google’s new filter checks
A hostname identifies the website associated with an event, such as www.example.com or shop.example.com. The Include option lets you define the hostnames your property should accept. Events carrying other hostnames are filtered out.
According to Google’s release notes, events with empty hostnames are also blocked. Events sent through Measurement Protocol are exempt from the Include filter.
Google introduced hostname exclusion in June. September’s addition lets businesses maintain an approved list instead of updating an exclusion list whenever another unwanted hostname appears.
Will it help with the Singapore traffic?
The useful check is the hostname associated with suspicious events. If those events carry an unapproved hostname, the allowlist can filter them. If they carry an approved hostname, the hostname condition alone gives the filter no reason to reject them. Measurement Protocol events bypass it altogether.
That means a country-level spike is a starting point for investigation. The filter does not assess whether someone in Singapore is a genuine reader or a bot; it checks the hostname against your rules.
For publishers experiencing the pattern described in our earlier report, examine the suspicious traffic’s hostnames before expecting this setting to solve it. Google’s announcement does not establish that the feature addresses that particular wave.
Test before permanently excluding events
Google places the controls under Admin → Data collection and modification → Data filters. Creating a filter requires Editor access or above.
Its hostname-filter guidance recommends using the Testing state and waiting 24–36 hours before validating the results. Testing marks matching data with the “Test data filter name” dimension so it can be examined before activation.
Check every legitimate website and subdomain intended to feed the property, including separate shops or campaign sites. Leaving one out could cause real activity to disappear from reporting when the filter becomes active.
Google’s data-filter documentation says excluded events are permanently discarded and will never be available in Analytics or BigQuery. Filters affect new incoming data, so historical spam remains in existing reports.
Record when you activate the filter. A subsequent traffic decline may partly reflect the events you have stopped collecting, which matters when comparing audience performance before and after the change.
Start the conversation by posting the first comment