

Google Ads says Data Manager will stop requiring SHA-256-hashed customer data from November 16, 2026, and support encrypted customer data by default. The notice covers offline data used for Customer Match and enhanced conversions.
A Google email shared by Anthony Higman names CRM connections, cloud storage imports, direct file uploads and the Data Manager API. It does not say whether existing prehashed uploads will remain supported after the change.
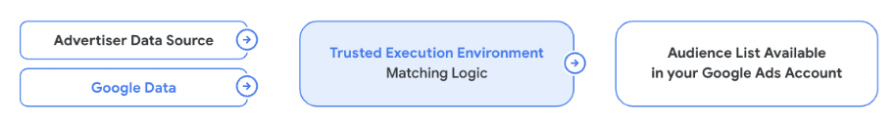
Google says the new process will decrypt, normalize and match data with Google accounts inside a hardware-isolated trusted execution environment, or TEE. The company attributes the change to better matching and fewer formatting errors before hashing, without giving an improvement figure.
Formatting moves closer to the matching step
Under the API’s current formatting instructions, an email address must be normalized before it is hashed. That includes converting it to lowercase and removing specified characters; phone numbers have their own required format.
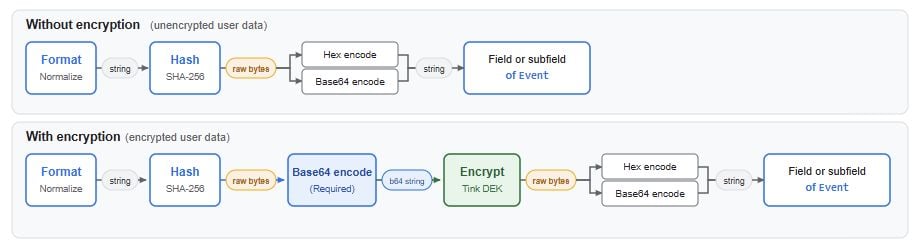
For example, the documented Gmail rules remove dots and plus-address suffixes before hashing. Preparing a record differently produces a different input to the hash, which is why Google links the November change to formatting discrepancies.
Some Data Manager connections already handle preparation for advertisers. Google’s Smart hash documentation says the tool can normalize, hash and encode relevant personal-information fields automatically. The notice therefore affects more than people who manually prepare upload files.
The confidential matching system already uses a TEE for supported connections. Its documentation describes matching advertiser data against Google data inside that environment, with an audience list returned to the Ads account.
Keep the current upload rules until your connection changes
The API guide still instructs developers to hash email addresses and phone numbers, including before its optional encryption step. The future-dated email supplies no replacement request format or instructions to remove hashing from an existing integration now.
For a team sending CRM records into Google Ads measurement, the useful pre-November check is which connector prepares those identifiers. Ask the integration owner whether formatting and hashing happen in the CRM export, the connector or Google’s import process.
That identifies the component that might need changing when implementation guidance arrives. Keep a dated record of upload diagnostics and match results before the transition, so a change in matching can be investigated separately from a change in campaign delivery.
Start the conversation by posting the first comment